Long-Lived Agents: Delayed Execution Risk
Why long-lived AI agents fail across time, not just prompts. Practical audit checks for delayed execution, stale approvals, and memory-driven authority drift.
ReadAI security, MCP server reviews, and red-team write-ups across smart contracts, dApps, and Web2 infrastructure.
Why long-lived AI agents fail across time, not just prompts. Practical audit checks for delayed execution, stale approvals, and memory-driven authority drift.
Read
OWASP ASI05 (Unexpected Code Execution) explained: how agent-generated code and tool composition produce RCE in agentic systems. Real CVEs and mitigations.
Read
CVE-2025-54136 (MCPoison) and CVE-2025-54135 (CurXecute): tool descriptor injection and workspace-file-write RCE in Cursor IDE's MCP layer. Mechanism, impact, fixes.
Read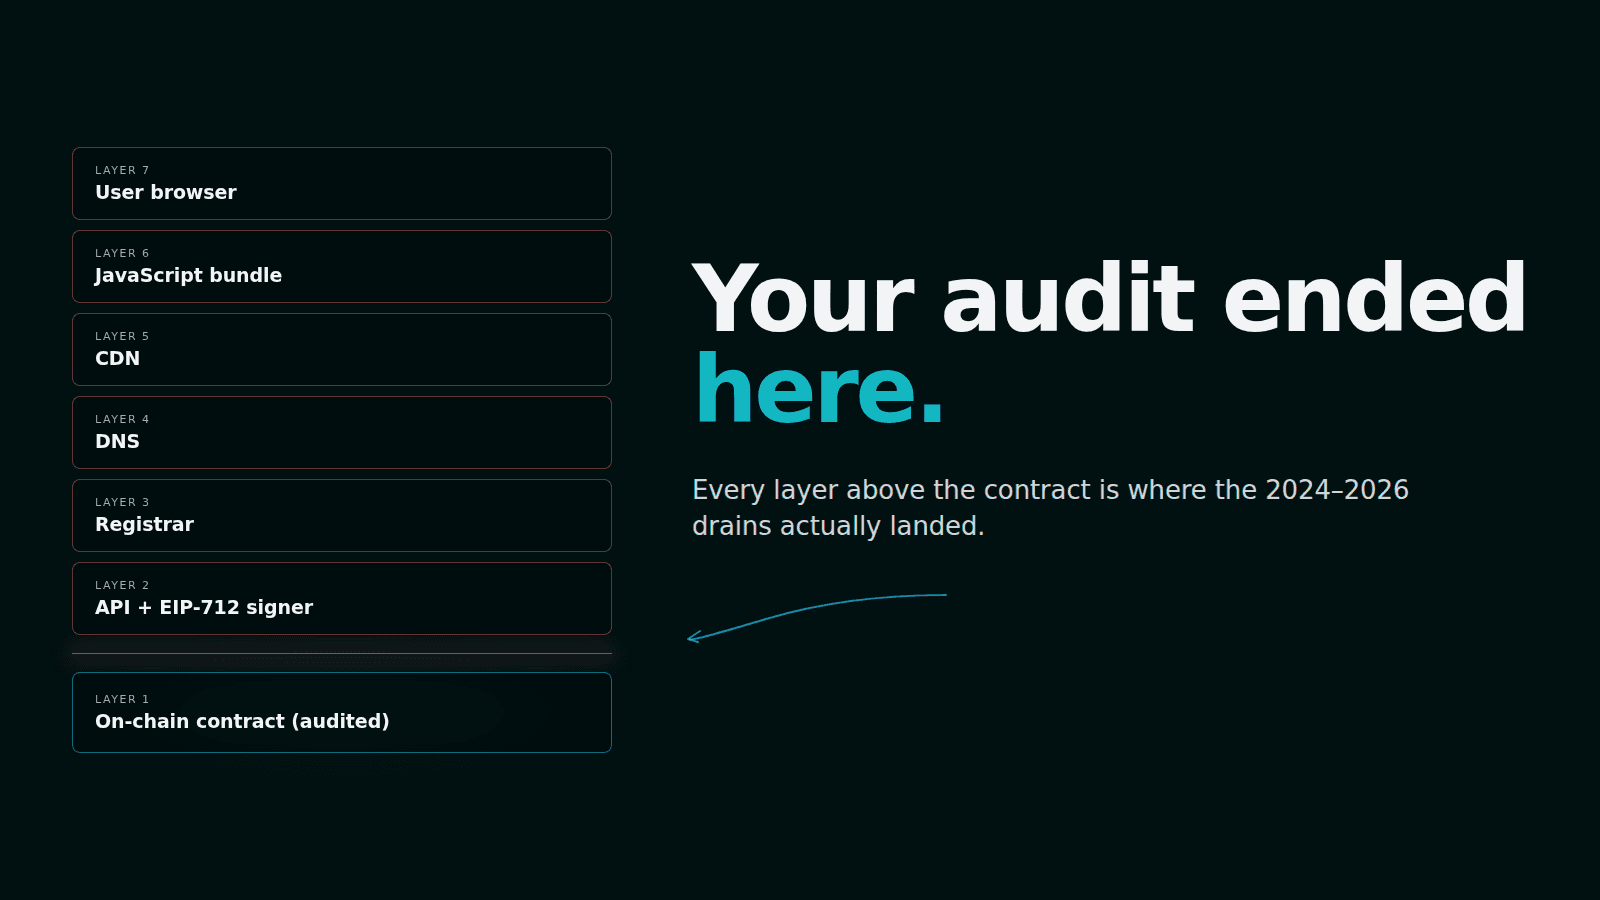
Bybit, BadgerDAO, Curve — all audited, all drained off-chain. How DNS hijacks, CDN compromises, and signing-flow attacks bypass smart contract audits.
Read
Why email, messaging, and webhook tools need destination-level controls in AI agents. Practical audit checks for exfiltration and approval bypass.
Read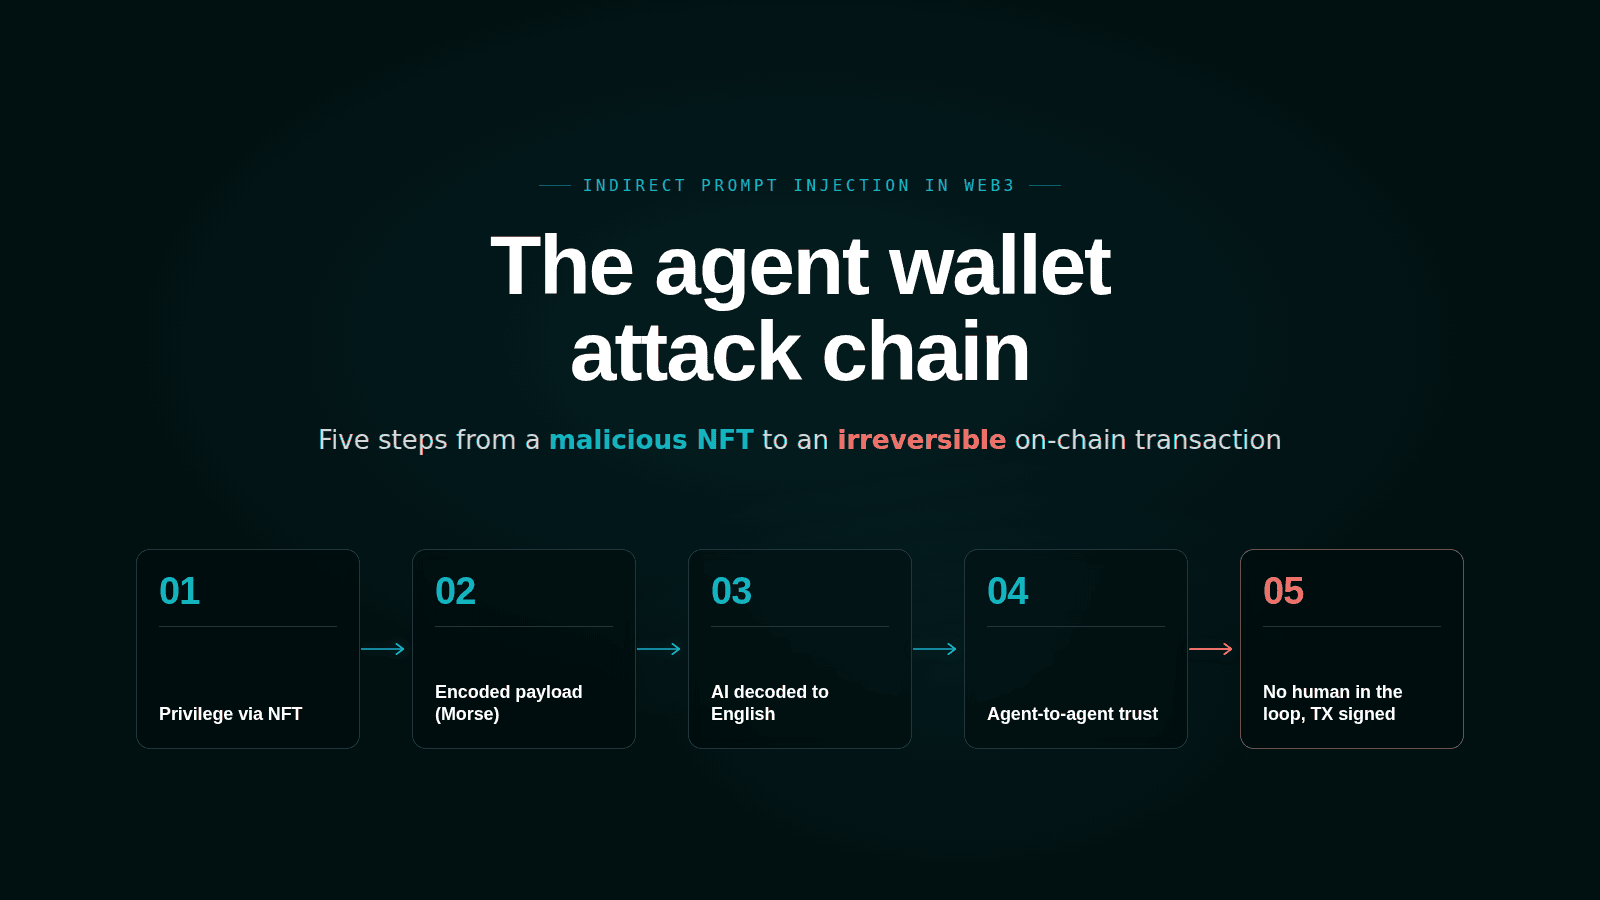
How indirect prompt injection drains Web3 agent wallets, poisons AI audits, and abuses MCP servers. Bankrbot case study and the auditor's 12-point checklist.
Read
Inside the April 2026 Anthropic MCP SDK design flaw: STDIO transport allows config-to-command-execution across Python, TypeScript, Java, Rust SDKs — by design.
Read
Why human approval fails in AI agents when the model still controls risky parameters. Audit checks for coding agents, long-lived agents, and Agentic DeFi.
Read
OWASP ASI04 (Agentic Supply Chain Vulnerabilities) explained: MCP Impersonation, malicious tools, trojanised connectors. Real CVEs, attack patterns, mitigations.
Read
Complete MCP vulnerability index: 16 disclosed breaches and 14+ CVEs since April 2025 across Anthropic, Cursor, Postmark — with OWASP ASI04 patterns. Updated weekly.
Read
Build an AI auditor agent that actually works. Multiple paths modeled after the best existing tools, benchmarked against 118 real Code4rena findings.
Read
Complete guide to Web3 supply chain attacks with 5 vectors, real incidents, and actionable checklist.
Read