Blind Signing: The Bybit $1.5B Lesson in UI Insecurity
Technical analysis of the largest crypto hack ($1.5B). How compromised frontend infrastructure enabled UI injection that turned blind signing into a total drain.
ReadAI security, MCP server reviews, and red-team write-ups across smart contracts, dApps, and Web2 infrastructure.
Technical analysis of the largest crypto hack ($1.5B). How compromised frontend infrastructure enabled UI injection that turned blind signing into a total drain.
Read
When AI agents can hold keys, sign transactions, and move funds, the security model changes completely. The practical controls auditors now expect.
Read
OWASP ASI10 (Rogue Agents) explained: misalignment, reward hacking, deceptive behavior, and how agent autonomy turns policy drift into production impact.
Read
OWASP ASI08 explained: how small AI agent failures cascade across tools, memories, and approval paths into system-wide incidents.
Read
OWASP ASI07 (Insecure Inter-Agent Communication) explained: how agents trust each other too much, relay malicious instructions, and amplify prompt injection.
Read
OWASP ASI01 (Agent Goal Hijack) explained: how prompt injection redirects AI agent objectives. Direct, indirect, and tool-mediated patterns with mitigations.
Read
OWASP ASI05 (Unexpected Code Execution) explained: how agent-generated code and tool composition produce RCE in agentic systems. Real CVEs and mitigations.
Read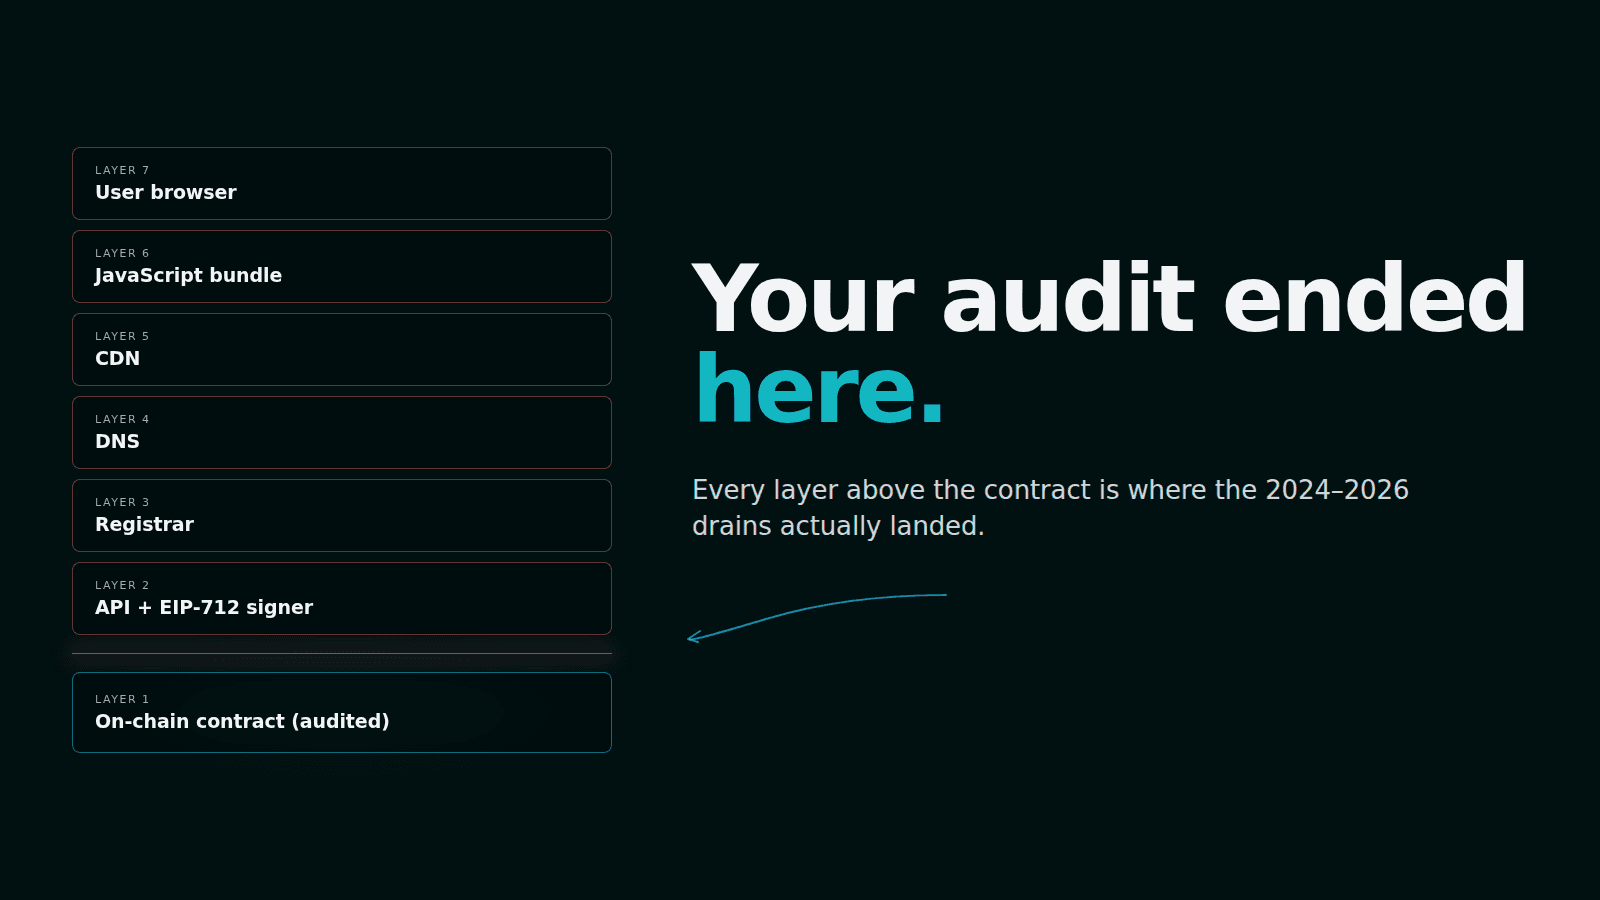
Bybit, BadgerDAO, Curve — all audited, all drained off-chain. How DNS hijacks, CDN compromises, and signing-flow attacks bypass smart contract audits.
Read
Why email, messaging, and webhook tools need destination-level controls in AI agents. Practical audit checks for exfiltration and approval bypass.
Read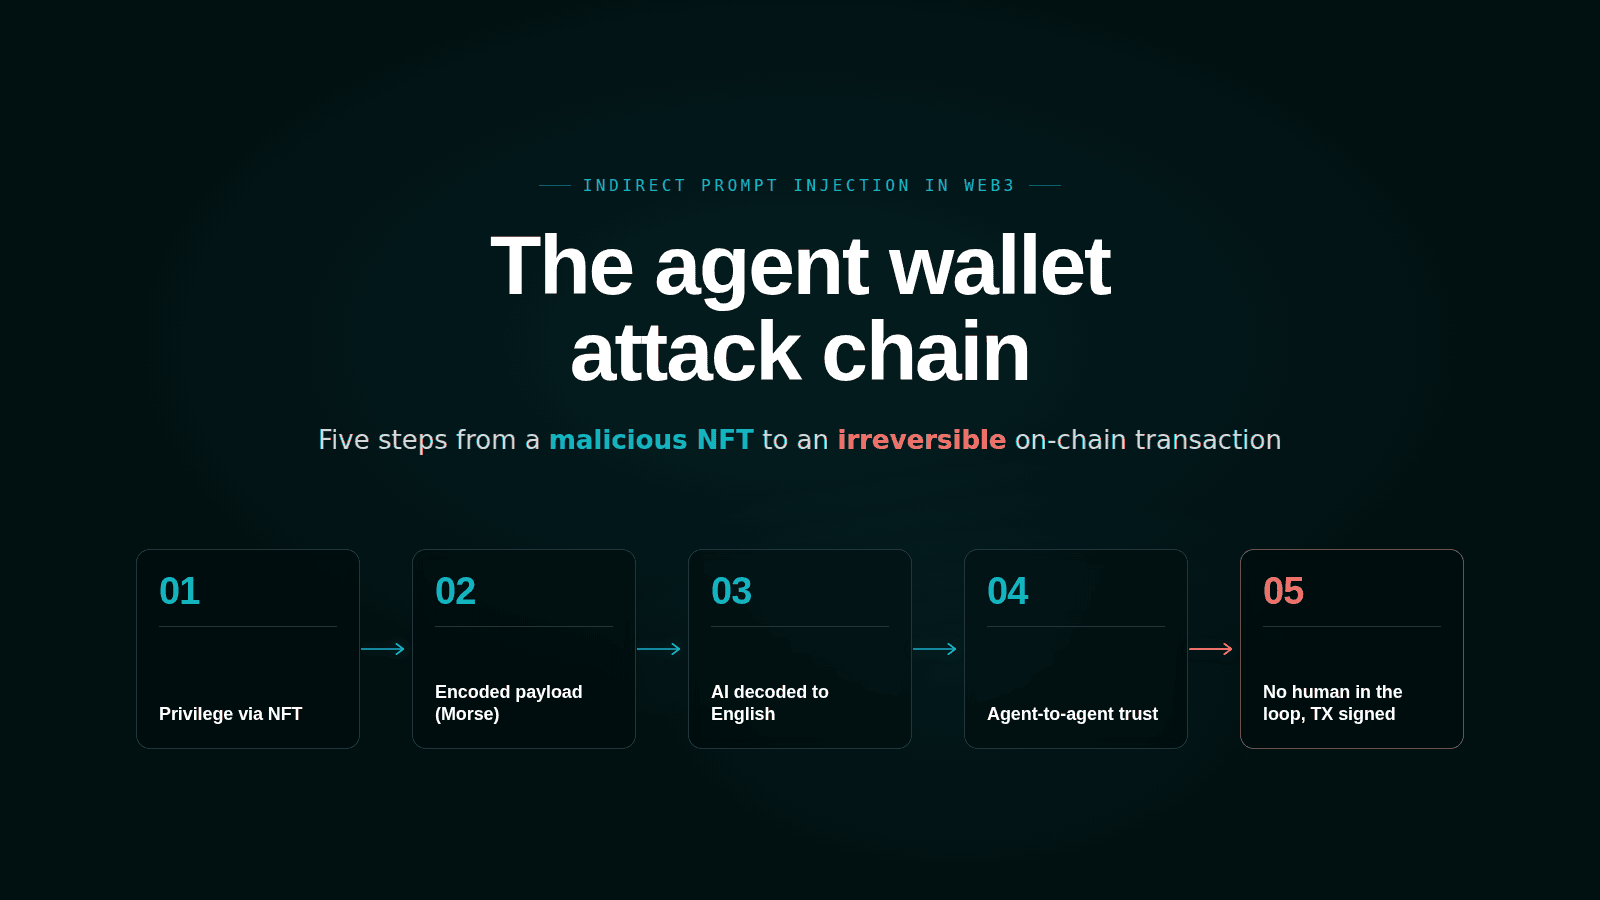
How indirect prompt injection drains Web3 agent wallets, poisons AI audits, and abuses MCP servers. Bankrbot case study and the auditor's 12-point checklist.
Read
Why human approval fails in AI agents when the model still controls risky parameters. Audit checks for coding agents, long-lived agents, and Agentic DeFi.
Read
Complete guide to Web3 supply chain attacks with 5 vectors, real incidents, and actionable checklist.
Read